by Chris Cleveland | Oct 14, 2026 | blog, phish
Anatomy of a Phish · Threat Research How Tech-Support Scams Buy Their Way Onto Your Screen An analysis of how fake Microsoft Support pages are delivered through social, native and programmatic advertising, and why that delivery path evades email security and domain...
by Chris Cleveland | Jul 11, 2026 | blog, phish
Ask a security team where phishing lives and the answer is reflexive: the inbox. That is where the budget goes — secure email gateways, DMARC enforcement, URL detonation sandboxes, banner warnings, awareness training built around “check the sender.”...
by Chris Cleveland | Jul 7, 2026 | blog, phish
Amazon’s Prime Day wrapped on June 26th — and the Amazon phishing wave around it is a case study in how attackers sidestep corporate email security. Leading up to the fourth of July weekend, PIXM observed a surge of post-sale lures — refund, delivery problem,...
by Chris Cleveland | Jul 3, 2026 | blog, phish
The message looks harmless — a wedding invitation, a shared card, a document someone wants you to see. It’s wedding season after all. Better yet, it arrives from a name you recognize: a colleague, a client, a friend. That is the whole trick. The social-invite...
by Chris Cleveland | Jul 2, 2026 | blog, phish
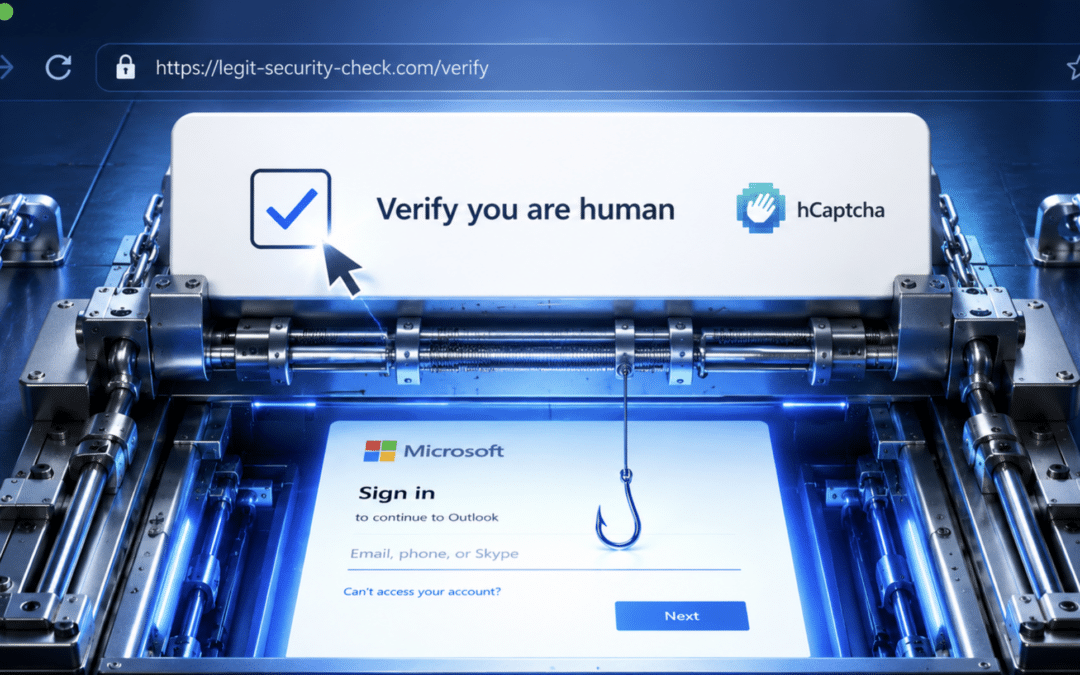
Between June 23 and 30, the phishing we detected in enterprise browsers clustered around two themes that also dominated the week’s security headlines: fake e-card “invitations” that harvest corporate credentials and fake “virus” warnings that push victims to...
by Chris Cleveland | Jun 25, 2026 | blog, phish
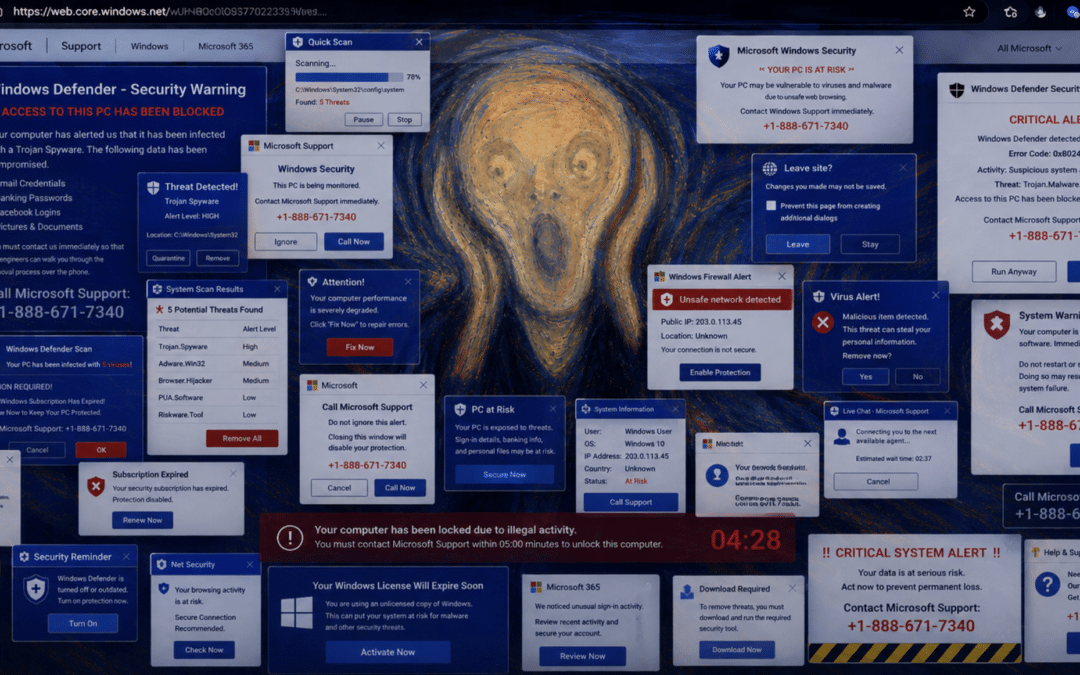
It didn’t start with an email. The user clicked a Facebook ad — a sponsored post that looked routine — and a tab opened to what looked like an official Microsoft Support page. Within seconds the browser locked up: a dialog they couldn’t dismiss, a...
Recent Comments